My bad, I didn’t think of that. My only thought was “$20 says this chucklehead won’t do squat” because we know.

- 1 Post
- 26 Comments
Joined 5 months ago
Cake day: April 20th, 2026
You are not logged in. If you use a Fediverse account that is able to follow users, you can follow this user.
https://grapheneos.social/@GrapheneOS Here you go, argue with GrapheneOS - it’s an open platform, go ahead and make a masto account and share your thoughts with them. Tell them what you think! The rep who handles their masto account is very well spoken and presents rebuttals of value so I advise you bring your A game.
 8·11 days ago
There are already instances doing this (and Mastodon ones as well), it’s a thing - there are warehousing no-user instances[1] But they could be blocked! We can’t have that, luckily…
…the Lemmy API and RSS feeds have no authorization around them for consuming the firehose of data; if I were a person doing this data gathering, I’d just passively monitor the firehoses off the top instances from random rotating IPs. Could and is most likely happening right now, can’t block them.
[1] I personally wrote a simple script which uses the fediverse observer info, grabs the XX most popular communities and builds a subscription import file to bootstrap a new Lemmy instance. wasn’t hard, just some curl and jq work.
 6·17 days ago
Put HE (dns.he.net) in your back pocket - they run a free DNS service which includes slave (do we still call it that?) service so that you can add their resolver as an ultimate failover / failback if your self hosted DNS takes a dive for whatever reason things break in our world.
Generally, hosting your own DNS “should” mean having a primary and secondary on separate AS networks, or at least different provider routes or locations. But if you’re doing all this from home, where is the second location for DR purposes… exactly? I sure don’t have one, power goes out here everything goes dark - in the old days everyone used to do this (share out tertiary DNS to each other) but it’s become a thing of the past in today’s world. HE can help fill that gap.
To your point - I use Gcore DNS and Bunny DNS for my stuff, as I mainly use online VPSes and don’t run racks of hardware at the house. The only things I physically selfhost at home are a pair of old laptops acting as storage servers which backup all my bytes and bits from online to some SSDs.

 23·1 month ago
I have not tried/used it (yet?), but the kids are building Radicle for this very purpose. It gets a fair amount of techie coverage (blogs, comments, etc.) but sits in unique space compared to, say, Forgejo (classic self-hosted git).
 1·1 month ago
mote absolutely understands the law, addie is creating and moving goalposts to support their tirade. The person I was responding to made a ludicrous statement, to which I refuted with observable evidence (laws).
It is obvious to any reasonable person I was referring to and talking about the common folding pocket knife, not kitchen knives or other fixed bladed implements. I may not have written “folding” and it was implied, that could have been better. Your choice to move to some other mental place to complain is your choice, not mine.
But let’s get to the meat of your off-kilter tirade - what I have stated and am referring to is an anomaly in the world of knives; the locking mechanisms (there are several designs) on a 3" folding pocket knife is there for user safety. If you have owned and operated pocket knives under force, they can and will twist in your hand. And without a locking mechanism, they can and will snap shut on your fingers and slice you up. I know this personally. It fucking hurts.
I am very aware the UK has banned such an object because they believe it will curtail knife violence. I feel this is trading an actual proven safety feature for “feel good” nanny law that probably don’t matter to someone intent on committing knife violence. It only harms the honest user of the pocket knife who wishes to not mutilate their fingers.
A three-inch blade is allowed provided it doesn’t lock in place; as long as it just folds away (like a swiss army knife) then it’s fine. Three-inch butterfly knife will get you in a lot of bother, though.
You go from from a nice pocket knife to a fucking butterfly knife, like holy shit there’s an entire world of cutlery between those two and you jump to some crazy extreme with butterfly knives. Those knives are actually curtailed by laws of their own (switchblades, butterfly knives and other “assisted open” cutlery is vastly illegal in many places in the world) as they tend to overlap with gang violence laws (“public nuisance” in the legal chapters). This is not the same mechanisms or designs as safety locks on a folding pocket knife used by regular people doing regular things.
The UK outlaws the safety knife (it’s designed for cutting seat belts, smashing a car window and other save your life things) I keep in my vehicle next to a flashlight, because it’s longer than 3" and has a locking mechanism. You are not using this thing for knife violence. (search “spyderco rescue knife”) But, this tool is illegal in the UK because of it’s features.
So yeah, I understand the law. But I also understand knives and cutlery as I’m interested in the steels used, so just happen to learn other things along the way. And to be fair, other countries have just as stupid laws about other things, including my own. I’m specifically discussing this one law and it’s irrelevant it’s the UK for purposes of discussion of the law itself banning a safety feature.
In the UK, a knife with a blade over 3" and/or any safety locking mechanism is illegal. This same extremely common knife is legal to carry (typical utility pocket knife) in a majority of other parts of the world.
So close! you have to do
cat < foo.txt:-) (/s)

Al, we need to optimize. Speed and efficiency to prevent Ctrl+C.
Write 16MB of zeros to the beginning of the boot device to overwrite the boot blocks (16MB being extra cautious, 8MB is fine) and if you want to double the roulette fun, have it fork in parallel and do the same thing to the EFI partition (if you have one). Extra credit: fork a 3rd time and write 16MB to the end of the disk, nuking the backup GPT structure sitting there. This can all be a fun inline “one-liner” to appeal to cut & pasters. curl pipe bashers.
It’ll happen so fast there’s no stopping it, their only way out now is to get the running system saved off that disk while it’s mounted.[1] But your nuke is invisible, how long until they find out trying to reboot? Devious Al, you’re just devious.
[1] there is a way to recover if you build identical machines, like VMs or VPSes - a tool such as gdisk can pull the table(s) off one to a file, which can be pushed onto another. We’ve recovered $customer mistakes at $ITjob doing this before, it works. It might not boot properly, but it can contain enough filesystem boundary information to be able to recover a partition manually (rescue).
It’s when you subsist on Lower Class Brats songs during the night hours.
Look, I touched the bride’s butt once at the reception. Never living that down am I?
GenX here, using the 80/20 rule 80% of my friend’s marriages (probably higher %) have ended in divorce. Typically after kids are involved. :-/
You can read and support all his art/comics via Mastodon and his store (gricklemart): https://mstdn.social/@grickle
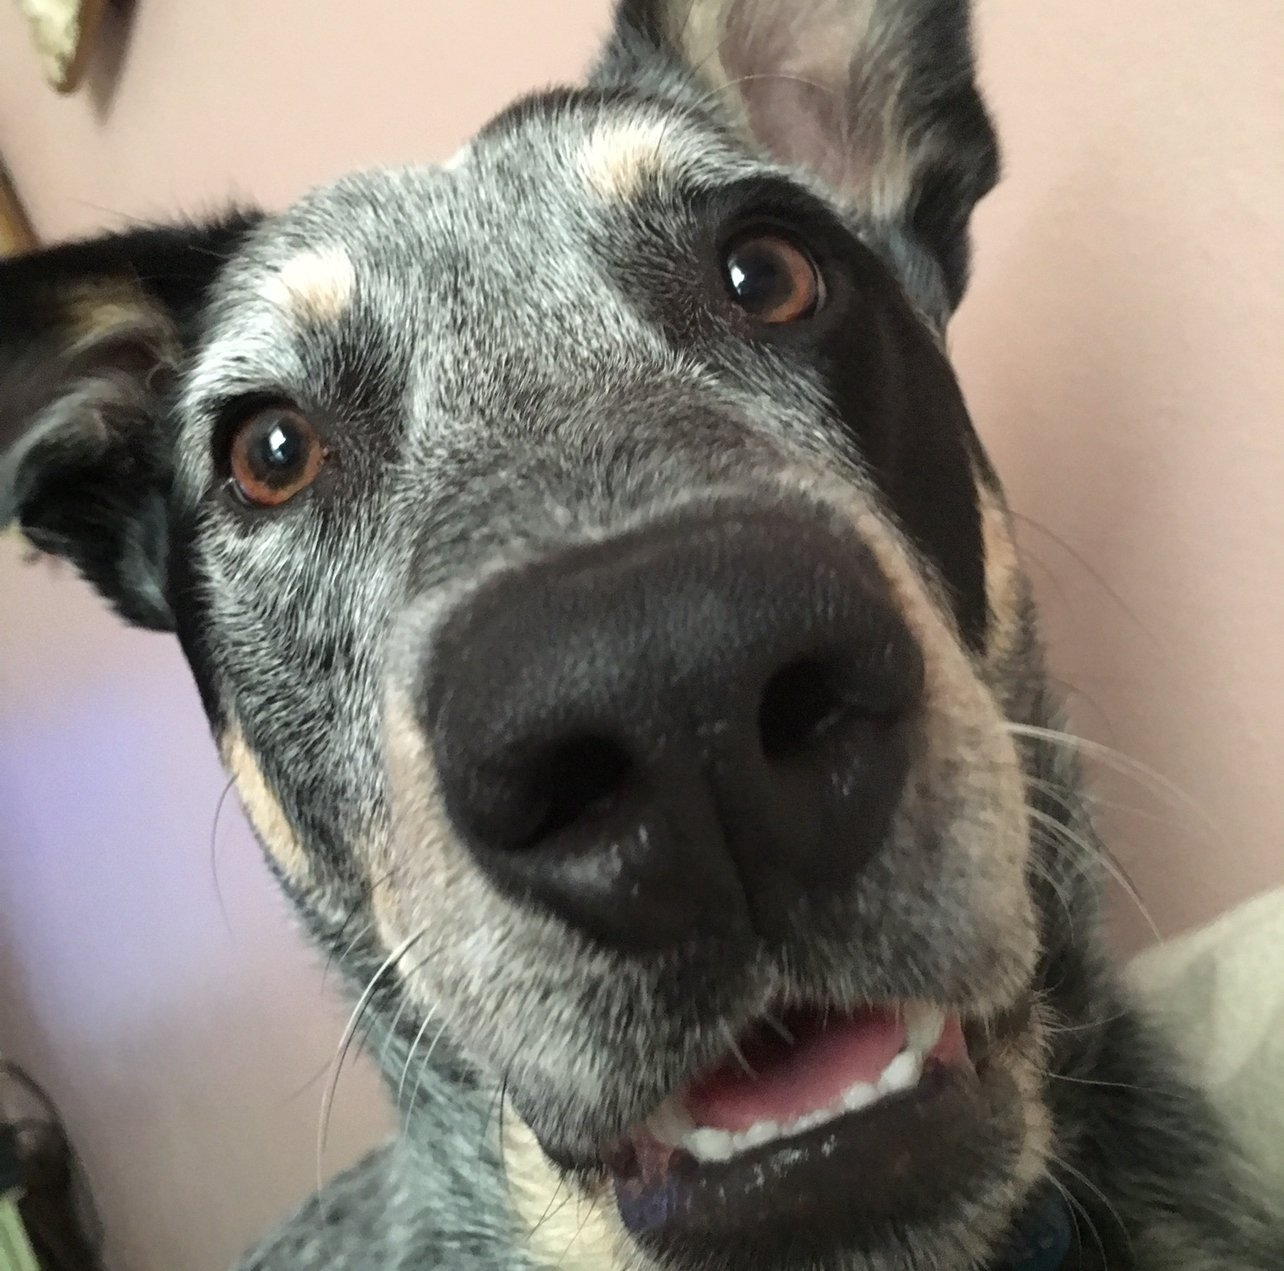
top: found sister’s sunglasses. 1753% good boy.
bottom: influencer
I am not trying to stand out excessively. … I don’t want something commonly mispronounced.
Me trying to come up with a new domain name for a website. Also add “easy to spell for 5th graders” to the list because repeating it to someone on the phone is painful sometimes and they still get it wrong.
My immediate thought: the paperwork system of the world would fail. Correcting an extremely unique misspelled name (let’s say it’s two letters transposed) falls into that weird bucket of “close enough typos” that the OP would never recover. I’d be worried most about the financial systems screwing me over.
IMHO, best to change to something clearly different so that the paperwork world is given a clear indication of intentional change. Broadcast the intent loud and clear to force systems to change and not ignore it as “some stupid typo.” $0.02
edit: sorry replied to the wrong comment my bad, meant the parent
I see folks mentioning going back to their dormant LFM accounts. The Metabrainz Foundation has a project ListenBrainz, a more open FOSS style version; if you’re going to spin some scrobbling cycles maybe check it out:
(I stopped scrobbling years ago, privacy concerns)
It sounds good but in practice it doesn’t work out; laptops sleep, people put their phones on airplane at night, whatever happens in life. The “best” solutions use some sort of cache-and-forward relay (thinking like DeltaChat relays, or I hear SimpleX is adding them) but I think most end up looking at Snikket (xmpp) or Matrix for the group management etc. on a central server. The Disroot group uses “Movim” which is XMPP highly customized to a social experience.
I use DeltaChat with friends and there’s a lot of things you can’t do because it’s essentially P2P with caching relays - like Jami, all control and data is stored on the device(s). If all you’re looking for is a Signal replacement it’s great (and why we use it), but if you want good group social controls you gotta go the central server route.
I think Jami here could do with caching relays like Delta has, could move this project to the next level.